front page
    Custom Security Headers PrestaShop Module | MayaWeb
    front page
    Custom Security Headers PrestaShop Module | MayaWeb

    Custom Security Headers

    €40.00
    No tax

    Protect your store against XSS, Clickjacking, and data breaches by injecting professional HTTP security headers. Instantly improve your security audit rating and boost customer and search engine trust. 🛡️🔒

    Close
     

    Elevate your PrestaShop security to professional standards with Custom Security Headers! 🚀

    Online store security depends on much more than just having an active SSL certificate. Modern browsers require explicit and strict instructions (HTTP headers) to know how to safely process and render your e-commerce content. Without them, your website remains vulnerable to critical attacks that can directly compromise your customers' sensitive data.

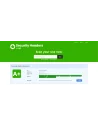
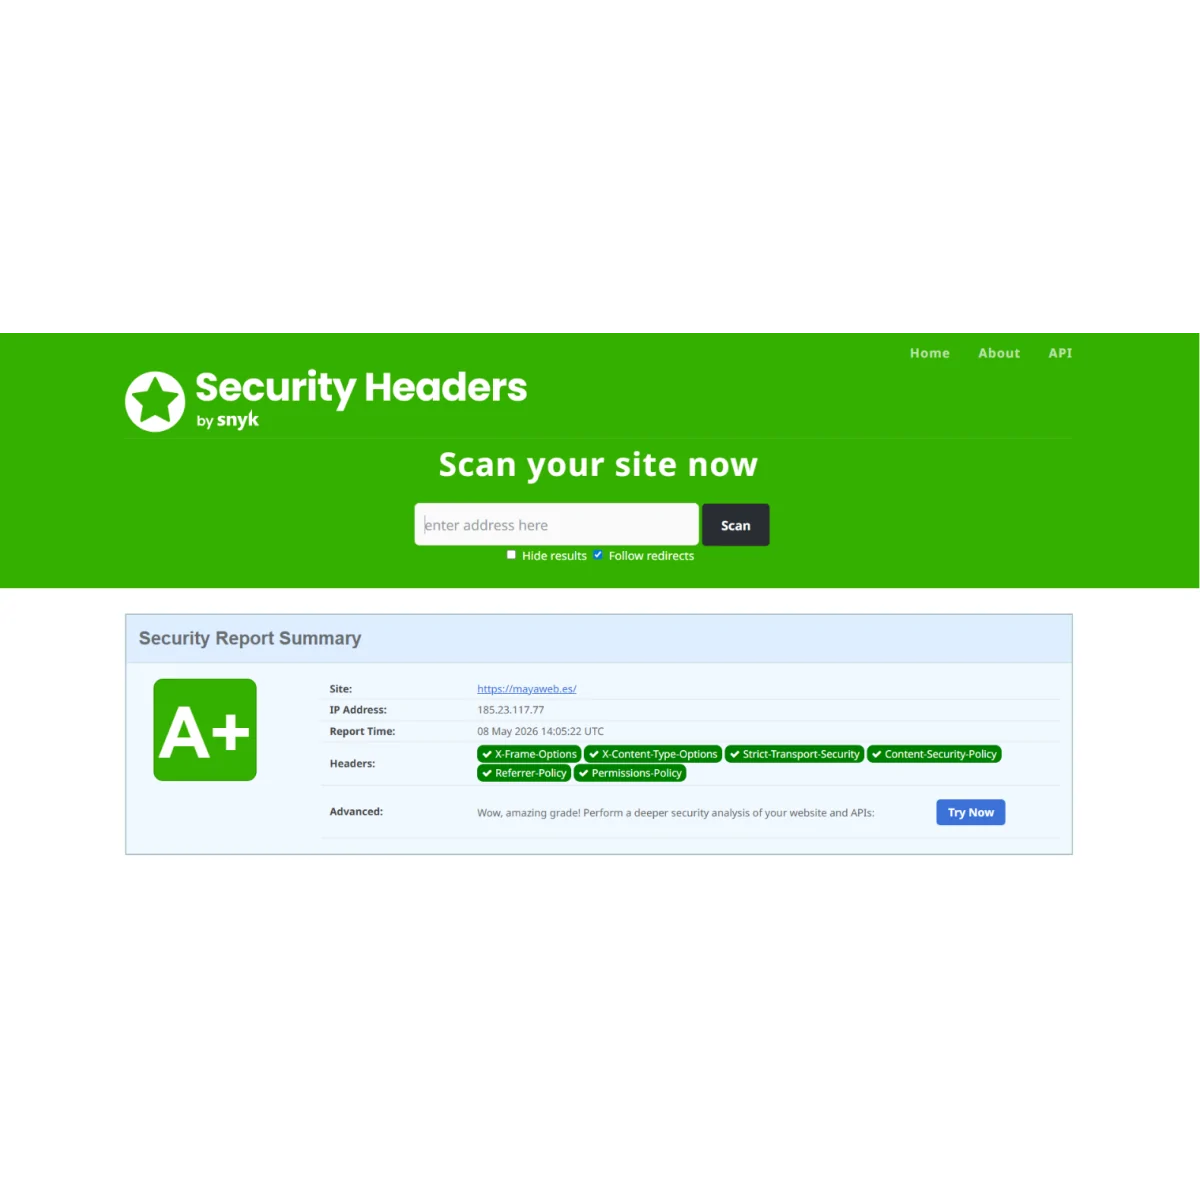
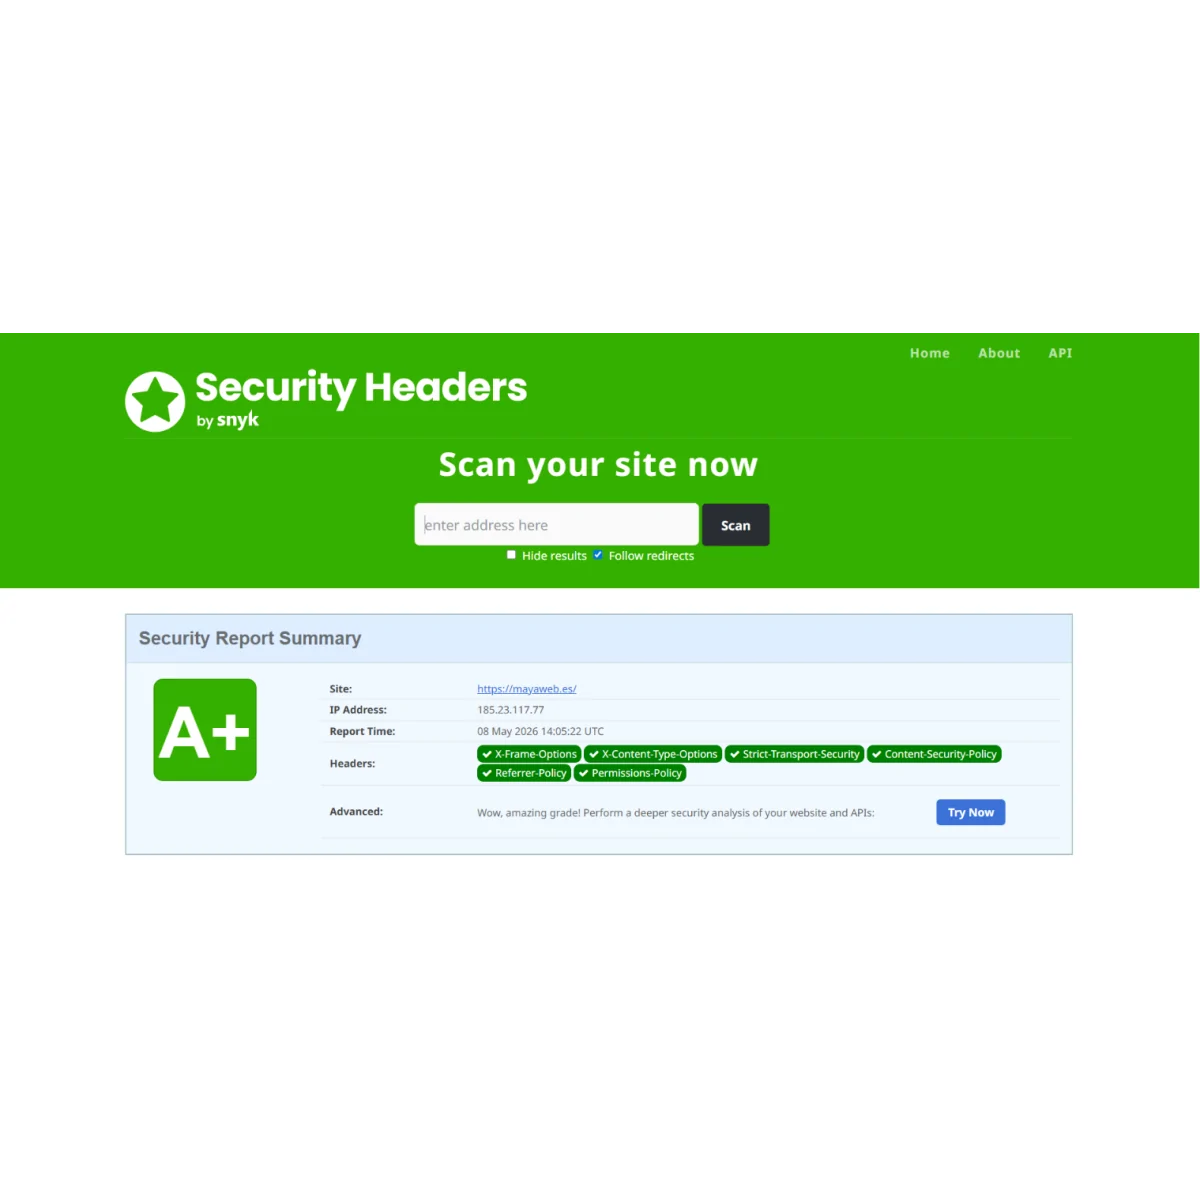
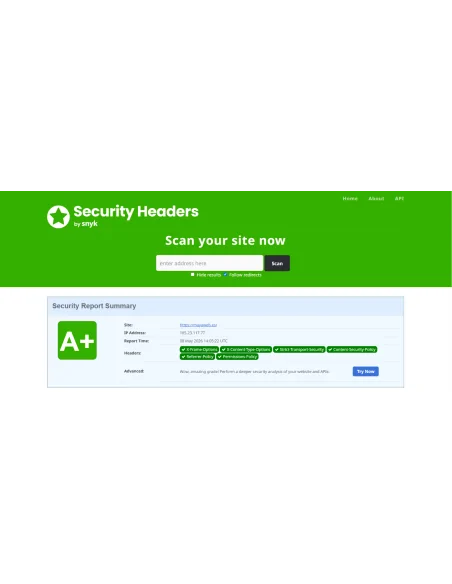
    Many hosting servers do not include these security headers by default, resulting in poor grades (such as D or F) on external audit tools like SecurityHeaders.com. This module is the ultimate tool to instantly achieve an A+ rating, reinforcing trust among your buyers, payment gateways, and search engines.

    🛡️ Comprehensive Protection Against Vulnerabilities:

    • X-Frame-Options (SAMEORIGIN / DENY): Protects your store from Clickjacking attacks, preventing cybercriminals from embedding your website into invisible frames to steal clicks or credentials.

    • X-XSS-Protection: Activates the browsers' native filters against malicious code injections (Cross-Site Scripting).

    • X-Content-Type-Options (nosniff): Forces the browser to strictly respect the declared MIME type, preventing dangerous files disguised as images or scripts from executing.

    • Strict-Transport-Security (HSTS): Strictly enforces all communications over secure HTTPS, mitigating protocol degradation attacks (MitM).

    • Content-Security-Policy (CSP): Automatically upgrades insecure requests (upgrade-insecure-requests), completely eliminating annoying "mixed content" warnings in the browser.

    • Referrer-Policy & Permissions-Policy: Safeguards your outbound traffic privacy and restricts access to device hardware APIs (like camera or microphone) that your store does not need to use.

    🔄 What's New in the Latest Version ($v1.2.0$):

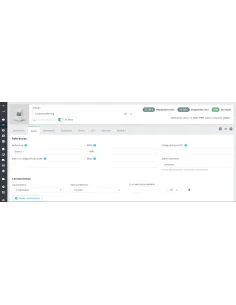
    • Dynamic Visual Configuration Panel: Forget about manually editing critical files like .htaccess or tweaking server configurations. You can now activate, deactivate, or customize the values of each header using simple switches directly from your PrestaShop Back-Office.

    • Smart Cross-Origin Isolation Management: Features native control over modern isolation policies (COEP, COOP, and CORP).

    • Conflict Prevention & Multimedia Support: The COEP header is disabled by default, and the module integrates smart alerts into its interface. This safely prevents YouTube videos, Google Maps, or external payment gateways from breaking or being blocked.

    • Advanced Header Injection (PrestaShop Hooks): Implements the actionDispatcher hook, ensuring that the security injection works flawlessly on both legacy PrestaShop controllers and modern Symfony-based controllers.

    • Enhanced Anonymity Against Attackers: Includes an option to remove the X-Powered-By header, preventing malicious users from gathering technical information about your server's PHP version.

    • Extended Compatibility: Developed under PSR-12 standards

    Compatible with
    Ps 1.7
    Ps 8x
    Ps 9x
    Publication date
    08 May 2026
    Last version
    1.2
    Last update
    08 May 2026
    25 May 2026
    Category
    Security
    SEO
    MAYA-SEC-HEADERS
    1000 Items
    No reviews

    Product Questions

    No questions yet. Be the first to ask a question!

    Ask a Question

    1.2 -
    Versión: 1.2.0
    Fecha: 25 de mayo de 2026
    
    Últimos Cambios en esta Actualización:
    ======================================
    
    1. Panel de Administración Integrado:
       - Se añadió un panel de control interactivo en el módulo usando PrestaShop HelperForm.
       - Ahora es posible activar o desactivar de forma independiente cada una de las 10 cabeceras HTTP de seguridad.
       - Permite personalizar el valor de cada cabecera directamente desde campos de texto.
    
    2. Solución de Carga para Vídeos de YouTube e Iframes:
       - Se desactivó por defecto la cabecera "Cross-Origin-Embedder-Policy" (COEP) al instalar el módulo para evitar que el navegador bloquee recursos de terceros (como vídeos de YouTube, Google Maps o pasarelas externas).
       - Se añadió una alerta explicativa en la cabecera de la configuración del módulo que guía sobre cómo esta opción afecta a recursos externos si el usuario decide habilitarla.
    
    3. Parche para Servidores con 'escapeshellarg' Deshabilitado:
       - Se solucionó el error 500 que ocurría al usar el Modo Depuración en servidores que tienen bloqueada la función 'escapeshellarg' de PHP.
       - Se interceptó y sustituyó localmente para el recolector de datos de Symfony mediante el uso de sombras de espacio de nombres (namespace shadowing).
    
    4. Corrección y Limpieza de Estándares PrestaShop Addons:
       - Se actualizaron las cabeceras de licencia de los archivos siguiendo las directrices oficiales y evitando bloqueos de validación por regex.
       - El archivo .htaccess fue reestructurado para permitir la carga correcta de elementos estáticos (como el logo del módulo) evitando bloqueos 403.
       - Se formatearon todos los archivos a codificación UTF-8 sin BOM y saltos de línea Unix LF.
    
    1.1.0 +

    8 other products in the same category:

    ×
    Product Image

    Custom Security Headers

    Protect your store against XSS, Clickjacking, and data breaches by injecting professional HTTP security headers. Instantly improve your security audit rating and boost customer and search engine trust. 🛡️🔒

    front page
    Custom Security Headers